Article
6 min read
7 Top Identity Access Management Tools for Seamless Employee Permissions
IT & device management
Author
Dr Kristine Lennie
Last Update
November 12, 2026
Deel IT, Okta, Microsoft Entra ID, JumpCloud, CyberArk, SailPoint, and Ping Identity are options for automating user access. Okta and Entra ID focus on identity management, while SailPoint and CyberArk offer specialized governance and privileged access capabilities. Deel IT stands out by connecting HR-driven provisioning and deprovisioning with device management, security, and offboarding for global teams.
Managing employee access gets more complicated when people join, change roles, or leave. Each change means granting the right permissions, updating existing access, or making sure former employees can no longer log in. The right access management system automates these steps, helping IT teams enforce least privilege and keep access secure without handling every request manually.
This guide compares the leading access management platforms to help you evaluate which solutions truly automate workforce identity, and which still rely on manual coordination between HR and IT.
Disclaimer: The information in this article is for general guidance only. Product features, pricing, and availability may change without notice. While we aim to provide accurate and up-to-date information, Deel makes no guarantees regarding its accuracy or completeness and takes no responsibility for decisions made based on this comparison.
At-a-glance comparison
The table below shows the top identity and access tools, their focus, and key strengths.
| Tool | Primary focus | Ideal for | Key strengths |
|---|---|---|---|
| Deel IT | Workforce lifecycle-driven identity, access & device orchestration | Distributed and global teams managing complex joiner/mover/leaver workflows | HR-driven lifecycle automation across applications and devices, role-based access, single sign-on (SSO)/multi-factor authentication (MFA) integration, device enforcement, centralized visibility |
| Okta | Cloud identity, SSO & MFA enforcement | SaaS-heavy environments | Large application integration library, adaptive MFA, automated SaaS provisioning, strong cloud-first authentication |
| Microsoft Entra ID | Identity platform with Conditional Access | Microsoft-centric organizations | Deep Microsoft 365/Azure integration, conditional access policies, and entitlement management |
| JumpCloud | Directory services with cross-OS device management | Hybrid, mixed-OS fleets | Unified identity and device management, device policy enforcement, cross-platform directory control |
| CyberArk | Privileged Access Management (PAM) | Large, regulated enterprises | Credential vaulting, session monitoring, temporary privileged access, and strong security controls for high-risk accounts |
| SailPoint | Identity Governance & Administration (IGA) | Enterprises with strict audit requirements | Access certifications, segregation-of-duties enforcement, compliance reporting, and governance automation |
| Ping Identity | Federated identity & adaptive authentication | Hybrid, multi-domain environments | Enterprise SSO, adaptive MFA, federated identity management, partner and external user access |
How Deel IT handles automated access provisioning and deprovisioning
Deel IT connects workforce changes with application access, device management, and security workflows. Unlike managing access through separate HR, identity, and IT systems, Deel IT helps teams coordinate onboarding, role changes, and offboarding through connected workflows, reducing manual handoffs and the risk of missed access updates.
Deel IT complements existing identity providers rather than replacing their core authentication capabilities.
Deel IT
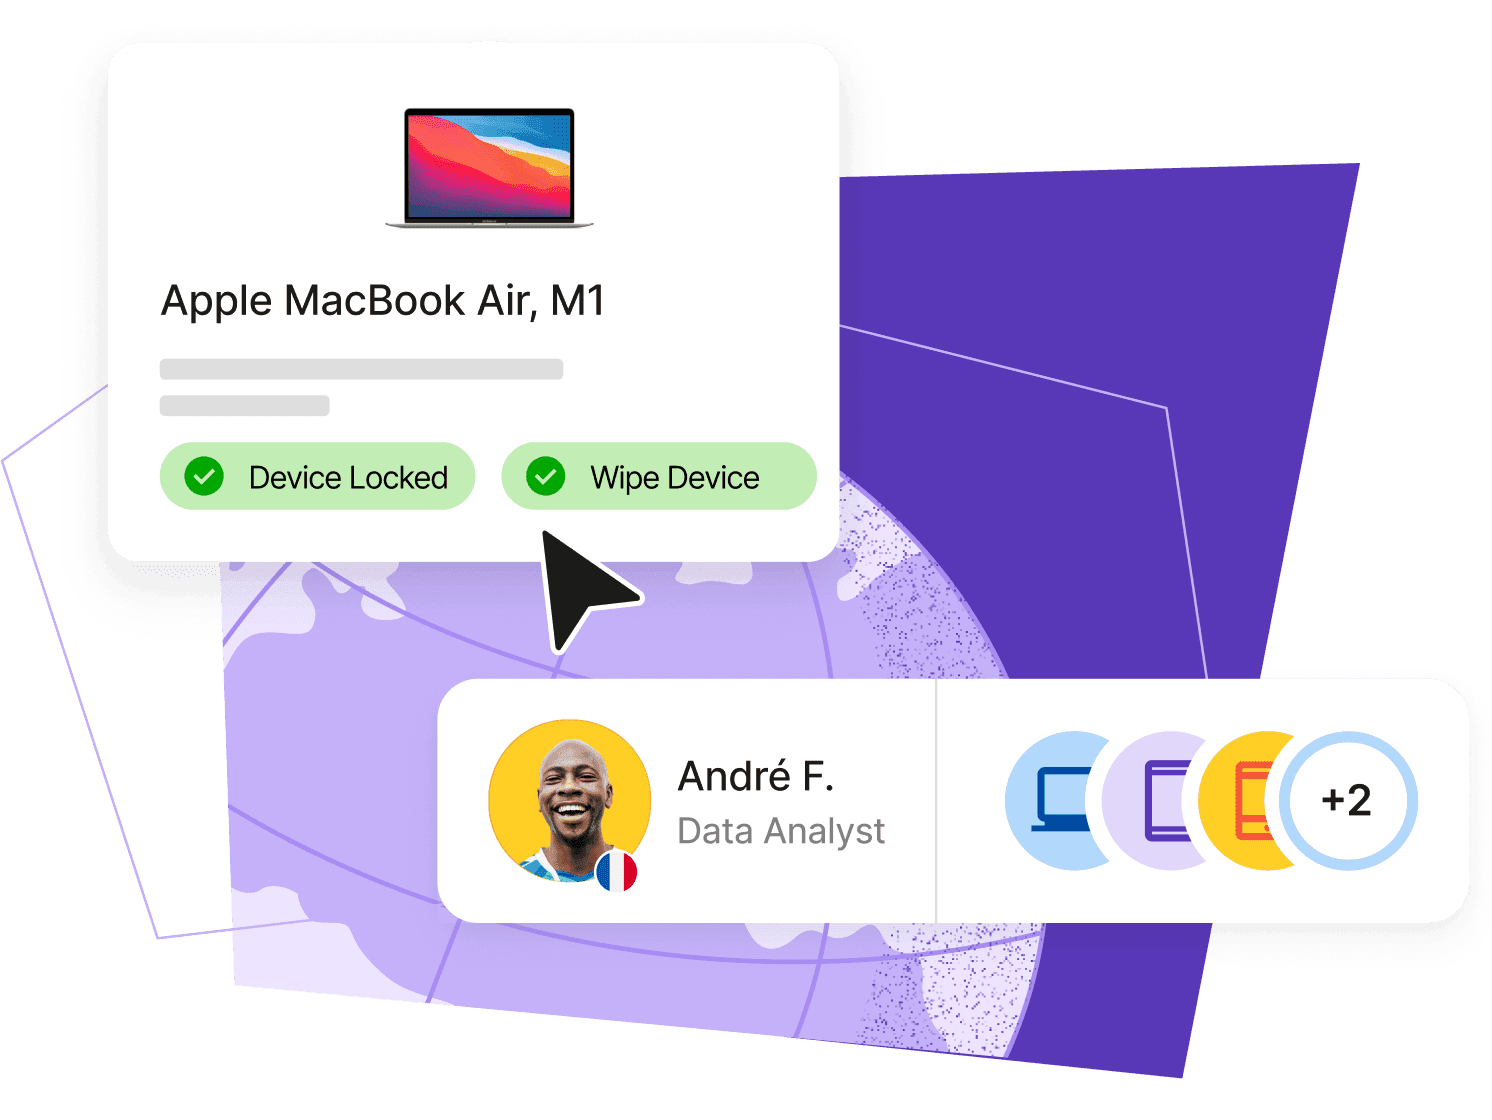
Deel IT unifies access provisioning, device lifecycle management, and employee lifecycle events—onboarding, role changes, offboarding—in one platform built for modern, global teams. When an employee's role changes, access updates automatically across apps and devices without manual tickets or IT handoffs.
Core capabilities:
Centralized SSO and access requests across the applications employees actually use.
Device provisioning, posture checks, and automated deprovisioning on exit.
Role- and policy-based workflows mapped to HR events for true least privilege.
Audit trails and reporting to demonstrate who had access to what, and when.
Best for: Organizations managing remote or internationally distributed teams that want HR, identity, and device management in a single workflow—particularly those already using Deel for global hiring or contractor management.
Limitations: Deel IT is not a standalone identity provider, so companies looking solely for SSO, MFA, or identity authentication will still need a dedicated solution. Its broader value comes from connecting identity tools with HR-driven access provisioning, device management, and IT operations.
What sets Deel IT apart: Many traditional identity platforms treat HR data as an integration layer rather than the trigger for access decisions. Deel IT uses HR events as the trigger, automatically keeping access policies aligned with who employees are, their roles, and where they work.
Employees get their laptops on time, they can start on day one versus day 20. I’m not troubleshooting, I’m not spending five hours a month on IT issues. And if I hire an employee outside the US and I need to deploy a laptop, I know it’ll get to them on time.
—David Khim,
Co-founder & CEO, Omniscient Digital
Identity Access Management
Seamlessly provision device and app access for global teams
As AI-powered fraud becomes more sophisticated, how do you know you're granting access to the right person? Deel Security helps businesses spot fake identities, deepfakes, and impersonation attempts before and after hiring, complementing traditional identity and access management with an added layer of fraud detection.
Okta
Okta is a cloud-based IAM platform that provides SSO, MFA, automated provisioning, and API access management.
Core capabilities:
Large application connector library spanning SaaS and developer tools.
Adaptive MFA with contextual risk signals.
SCIM-based HRIS provisioning and low-code lifecycle workflows.
Clean admin UX suited to SaaS-heavy environments.
Best for: Organizations that run primarily on SaaS and want a cloud-first authentication layer with minimal operational overhead and fast time-to-value on integrations.
Limitations: Companies looking to manage employee devices and IT operations alongside access management may need additional tools. Some advanced features also come at an extra cost, depending on the plan.
Microsoft Entra ID
Microsoft Entra ID (formerly Azure Active Directory) is an identity platform for Microsoft-centric organizations.
Core capabilities:
Native integration with Microsoft 365, Azure, and on-premises systems
Conditional Access with device posture and risk-based enforcement
Identity governance: access reviews and entitlement management
Best for: Organizations already standardized on Microsoft 365 and Azure.
Limitations: Companies using a mix of Microsoft and non-Microsoft tools may need extra setup or integrations to automate employee access across all their systems. Entra ID also works most naturally within the Microsoft ecosystem, which is worth considering if your company uses a range of platforms.
JumpCloud
JumpCloud is a directory-first platform that manages identity and devices across Windows, macOS, and Linux.
Core capabilities:
Central directory and SSO for mixed-OS devices
Preconfigured device and app access for onboarding
Device posture checks before granting access (patches, encryption)
Unified policies for Wi-Fi, LDAP, RADIUS, and system logins
Best for: Teams with mixed operating systems that want a single platform for identity, access, and device management.
Limitations: JumpCloud covers both employee access and device management, but companies with more complex requirements for access reviews and compliance reporting may need additional tools.
Resources for secure employee access management
Consistent access provisioning starts with clear policies and coordinated onboarding and offboarding processes. These free resources can help:
Onboarding & Offboarding Guide for Distributed Teams: Coordinate employee access changes, device security, and offboarding responsibilities.
Free IT Policy Template: Establish consistent security and access management policies.
IT Strategy Toolkit: 2026 Guide: Plan scalable IT processes as your workforce grows.
CyberArk
CyberArk focuses on privileged access management (PAM), securing high-risk accounts like admins, service accounts, and infrastructure credentials.
Core capabilities:
Secure credential storage with automatic rotation
Session monitoring for privileged accounts
Temporary, time-limited admin access
Endpoint and reauthentication controls for sensitive tasks
Best for: Large enterprises and regulated industries—financial services, healthcare, critical infrastructure—where privileged account abuse is among the highest-impact risks and auditors require detailed session evidence.
Limitations: CyberArk focuses on securing privileged access rather than managing everyday employee logins, so companies may still need a separate identity management system. Setup and ongoing management can also require more time and resources, particularly for smaller IT teams.
SailPoint
SailPoint provides identity governance by tracking and reviewing who has access to applications, data, and cloud resources. It automates access reviews, flags conflicting roles, and generates compliance evidence for audits.
Core capabilities:
Centralizes entitlements across applications and data
Automates attestation campaigns and access certification workflows
Detects policy violations and conflicting access roles
Produces compliance evidence without manual reporting
Best for: Large enterprises with complex access needs and strict audit requirements. SailPoint is typically deployed on top of an existing identity provider, with custom pricing.
Limitations: SailPoint can take time to set up, especially if a company uses many different applications. Smaller IT teams may also find it harder to manage because of its advanced features.
Ping Identity
Ping Identity provides SSO, adaptive authentication, and partner access management across cloud and on-premises systems.
Core capabilities:
SSO across applications and systems.
Adaptive MFA based on risk and context.
Policy enforcement for hybrid and Zero Trust setups.
Partner identity management for B2B access.
Best for: Enterprises with hybrid or multi-cloud environments and external partner access needs.
Limitations: Ping Identity may require extra configuration when connecting older applications and different identity systems.
How Deel IT automates provisioning and deprovisioning differently
Most identity platforms require manual work to connect HR data with IT systems—importing, syncing, and adjusting access across apps and devices. Deel IT makes the workforce lifecycle the foundation of access management, automating devices, access, security, and support across the worker lifecycle so IT teams can operate globally with consistency, control, and scale.
Here is how:
Automatic access management across apps and devices: Role-, location-, and entity-based provisioning ensures employees get the right access instantly, including SSO, MFA, and conditional access rules
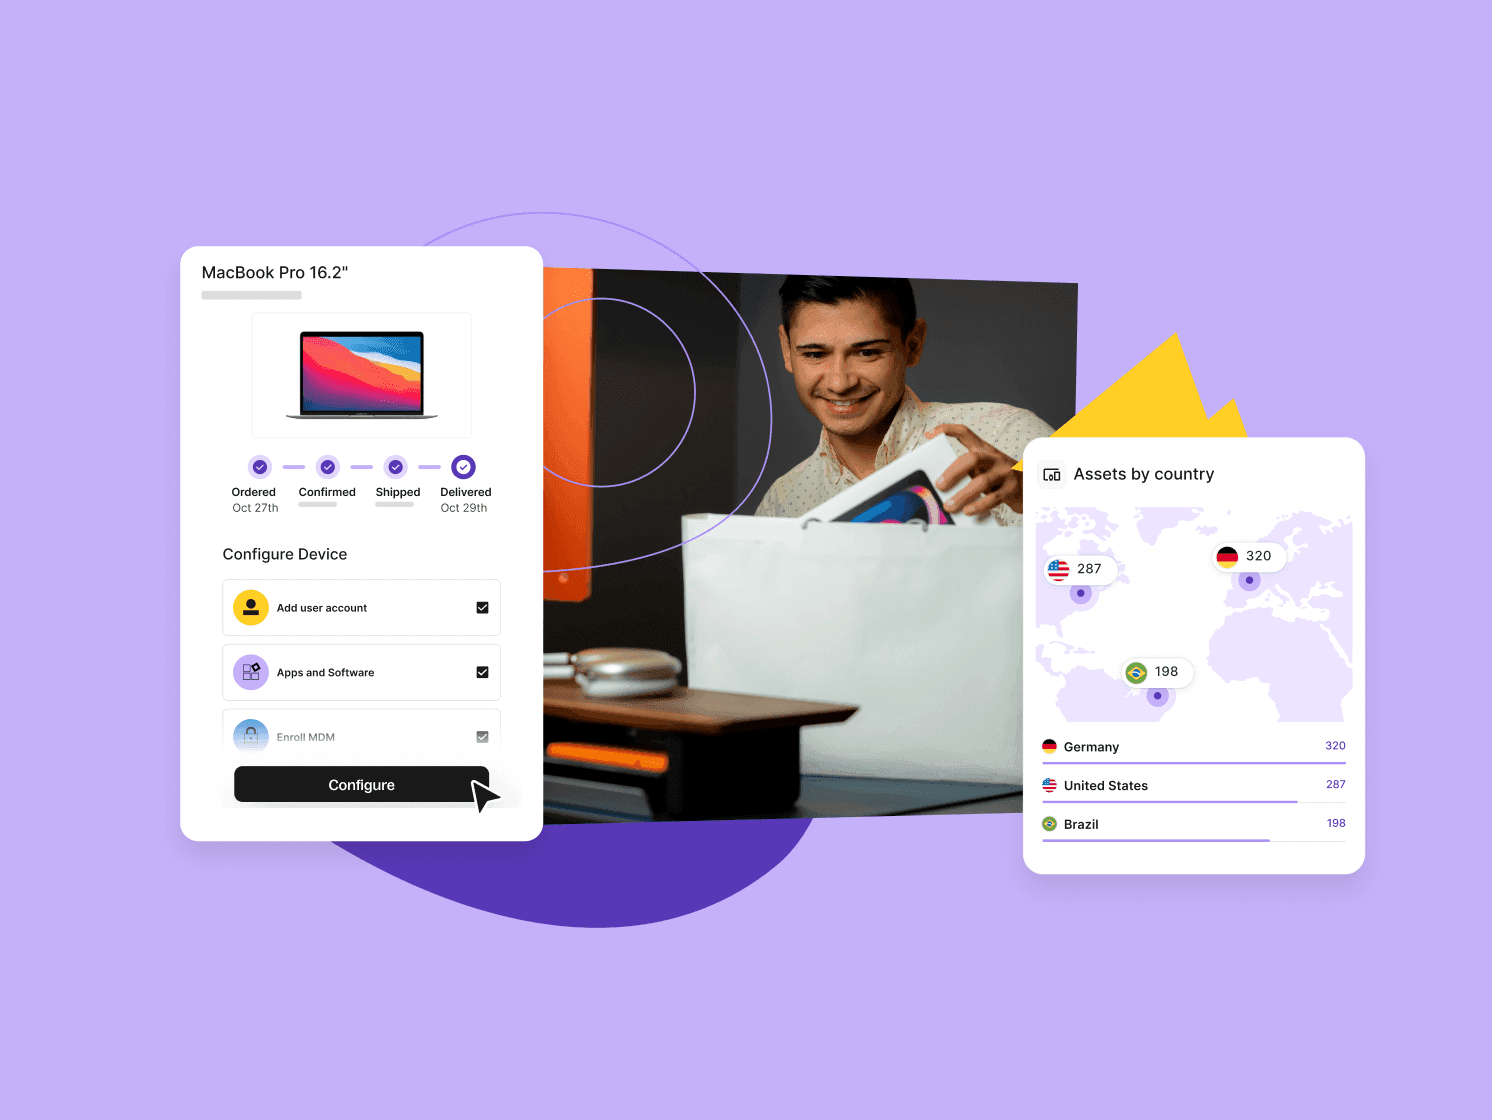
Devices and accounts ready on day one: Procure and ship pre-configured devices with required applications and security settings before employees start, with a 99.5%+ on-time delivery rate in 130+ countries
24/7 global IT support: Employees and IT teams can get help anytime, anywhere, keeping operations running smoothly without delays.
Real-time visibility in one dashboard: Track user access, device status, and entitlements across your organization without juggling multiple systems.
Automated lifecycle updates: Onboarding, promotions, transfers, and offboarding trigger immediate updates to access and device configuration via HRIS-connected workflow automations.
Secure offboarding: Access is revoked, accounts locked, and devices recovered and redeployed automatically when employees leave, reducing risk.
Less manual work for IT: Removes tickets, follow-ups, and repeated provisioning tasks, freeing IT to focus on strategy and security.
Book a demo with Deel IT to learn more.
Deel IT
Procure, deliver, manage, and secure devices anywhere
FAQ
Which access management systems can automate user provisioning and deprovisioning?
Options include Deel IT, Okta, Microsoft Entra ID, JumpCloud, CyberArk, SailPoint, and Ping Identity. Okta and Entra ID focus on identity and application access, while SailPoint and CyberArk offer specialized governance and privileged access capabilities. Deel IT goes further by connecting HR-driven access changes with device provisioning, security, and offboarding, making it a strong choice for growing and distributed teams.
What features should I prioritize in an access management system?
Look for HRIS integrations, automated onboarding and offboarding, role-based permissions, single sign-on (SSO), multi-factor authentication (MFA), and audit logs. Also check whether the platform supports your existing applications and can flag failed provisioning or deprovisioning actions.
How does automated provisioning and deprovisioning work when an employee joins or leaves?
An employee's start date, role change, or departure triggers a workflow through connected HR and identity systems. Based on predefined rules, the system creates accounts, adjusts permissions, or disables access in supported applications. This reduces manual requests and helps IT teams keep access aligned with employment status.
Can access management systems automatically revoke access from every application?
Not always. Automated revocation depends on the integrations and account management capabilities each application supports. For systems without direct provisioning integrations, IT teams may need alternative workflows and verification steps to ensure former employees no longer have access.
How does IAM improve security and compliance for distributed teams?
Identity and access management (IAM) helps companies apply consistent permissions, authentication requirements, and access policies across locations. Centralized logs and regular access reviews also make it easier to identify unnecessary permissions and provide evidence for security audits.
What's the difference between SSO and MFA?
Single sign-on (SSO) lets employees access multiple applications through a central login, while multi-factor authentication (MFA) requires additional verification to confirm their identity. They work together to secure access, but neither replaces automated account provisioning or deprovisioning.
What deployment options are available for IAM systems?
Cloud-based platforms are often easier to deploy and maintain, while on-premises solutions offer greater control over certain infrastructure and legacy integrations. Hybrid setups combine both approaches. The right model depends on your existing systems, security requirements, and IT resources.
About the author
Dr Kristine Lennie holds a PhD in Mathematical Biology and loves learning, research and content creation. She had written academic, creative and industry-related content and enjoys exploring new topics and ideas. She is passionate about helping create a truly global workforce, where employers and employees are not limited by borders to achieve success.