Article
7 min read
How to Choose and Implement an Access Management System for Automated Provisioning
IT & device management
Author
Dr Kristine Lennie
Last Update
November 12, 2026
Table of Contents
Step 1: Prepare by mapping your access lifecycle
Step 2: Set clear goals for automating user access when employees join or leave
Step 3: Identify your key selection criteria for an automated access management system
Step 4: Implement your AMS to automate joiner, mover, and leaver workflows
Step 5: Prevent friction and keep automation smooth
Step 6: Plan for the next 12–24 months
Streamline automated access provisioning and deprovisioning with Deel IT
FAQ
Okta, Microsoft Entra ID, and Google Workspace are strong options for automating user provisioning and deprovisioning when employees join, change roles, or leave. Deel IT goes further by connecting HR-driven access changes with device provisioning, security, and offboarding in one coordinated workflow, making it a compelling choice for companies managing growing or distributed teams.
Automated provisioning and deprovisioning streamline how employees gain and lose access to applications, keeping your systems secure, compliant, and efficient. The right access management system (AMS) makes this possible, automatically granting access on hire, updating it when roles change, and revoking it immediately on exit.
This step-by-step guide shows you how to map your access lifecycle, select the right AMS, implement automation, and plan for the next 24 months, so your team always has the access they need, without the manual overhead.
Step 1: Prepare by mapping your access lifecycle
Before implementing automation, take a clear look at how employees currently get access—and how it's removed when they leave.
Identify HR events (hires, transfers, terminations) that trigger access changes
Track which systems each event touches—HRIS, identity provider (IdP), key apps, and privileged assets
Note where automation exists and where manual steps create delays or risks
Capture audit trails for compliance visibility
Pro tip: Use this map to spot gaps—like orphaned accounts or slow deprovisioning—so your automated system fixes the right problems from day one.
Step 2: Set clear goals for automating user access when employees join or leave
Now that you've mapped your access lifecycle, define what success looks like. Automation should remove manual bottlenecks, reduce errors, and make access faster and more secure. Key outcomes to aim for:
Faster access request turnaround compared to manual processes
Reduced identity operations overhead through policy-driven automation
Shorter, more efficient audit cycles with centralized logs and evidence
Real-time HR event syncing so ex-employees lose access immediately—even to high-risk systems
Pro tip: Define measurable internal benchmarks (like average time-to-provision or deprovision) so you can track improvements after implementation.
Step 3: Identify your key selection criteria for an automated access management system
Before choosing an access management system, it's important to know exactly what to prioritize. This step helps you identify the critical features and capabilities your AMS must have to meet your organization's needs. Use the table below as a guide and check off each item as you evaluate potential systems.
| Key criteria | What to look for | Why it matters | |
|---|---|---|---|
| HR & IdP integration | Native HRIS connectors or, ideally, a system with built-in HR management (like Deel IT); IdP compatibility (Okta, Entra ID, Google Workspace); SCIM-based lifecycle automation | Ensures access updates automatically with HR events, reducing orphaned accounts and overprivileged users | ☐ |
| Legacy or disconnected applications | Automation agents for web-based tools; credential rotation for shared or legacy accounts; device-level controls when integration isn't possible | Lets you manage applications without modern APIs, avoiding manual processes and reducing access risks | ☐ |
| Governance & compliance | Automated access reviews and periodic sign-offs; immutable logs; prebuilt compliance reports (GDPR, SOX, HIPAA, SOC 2); separation-of-duties checks | Provides provable control for regulated environments | ☐ |
| Least privilege & access policies | Role- and attribute-based rules for joiner/mover/leaver flows; temporary or time-limited access; clear approval workflows and logging for sensitive accounts | Minimizes risk by granting only the access users need | ☐ |
| Deployment & scalability | Cloud, on-premises, or hybrid deployment; global coverage for distributed teams | Ensures your AMS works for your team's size, location, and regulatory requirements | ☐ |
How Deel IT handles automated access provisioning and deprovisioning
Deel IT connects HR data with application access, device management, and security workflows. Unlike standalone identity tools or manual processes that require separate coordination between HR and IT, Deel IT uses workforce changes to trigger connected provisioning and deprovisioning workflows, reducing manual work and the risk of missed access changes.
Step 4: Implement your AMS to automate joiner, mover, and leaver workflows
Once you've selected your AMS, configure it to automate provisioning and deprovisioning across every system employees use. This includes configuring access rules, event mappings, integrations, and workflows so the AMS can automatically grant, update, or revoke permissions across all connected systems.
How to implement:
Map user events to systems: Link joiner, mover, and leaver events in your HRIS to every system and application employees use, so the AMS knows when to grant or revoke access
Configure automated access rules: Set up role-based (RBAC) and attribute-based (ABAC) policies so the AMS automatically applies the right permissions for each user
Connect integrations: Ensure HR systems, IdPs, single sign-on, and other applications are linked to the AMS, enabling fully automated provisioning and deprovisioning
Validate compliance settings: Configure the AMS to enforce GDPR, SOX, HIPAA, and SOC 2 requirements, with audit logs and least-privilege enforcement built in
Run pilot scenarios: Test a small set of joiner, mover, and leaver workflows to confirm the AMS is granting and revoking access correctly
Set up temporary or sensitive access: Configure workflows for short-term elevated access with approvals, session logging, and automatic revocation
The piece on deploying software has been really easy. I might get a bunch of people asking for software, and I just say, hey, I’ve deployed it to everyone’s laptops. You don’t need to ask about this. And it’ll automatically update.
—David Khim,
Co-founder & CEO, Omniscient Digital
Identity Access Management
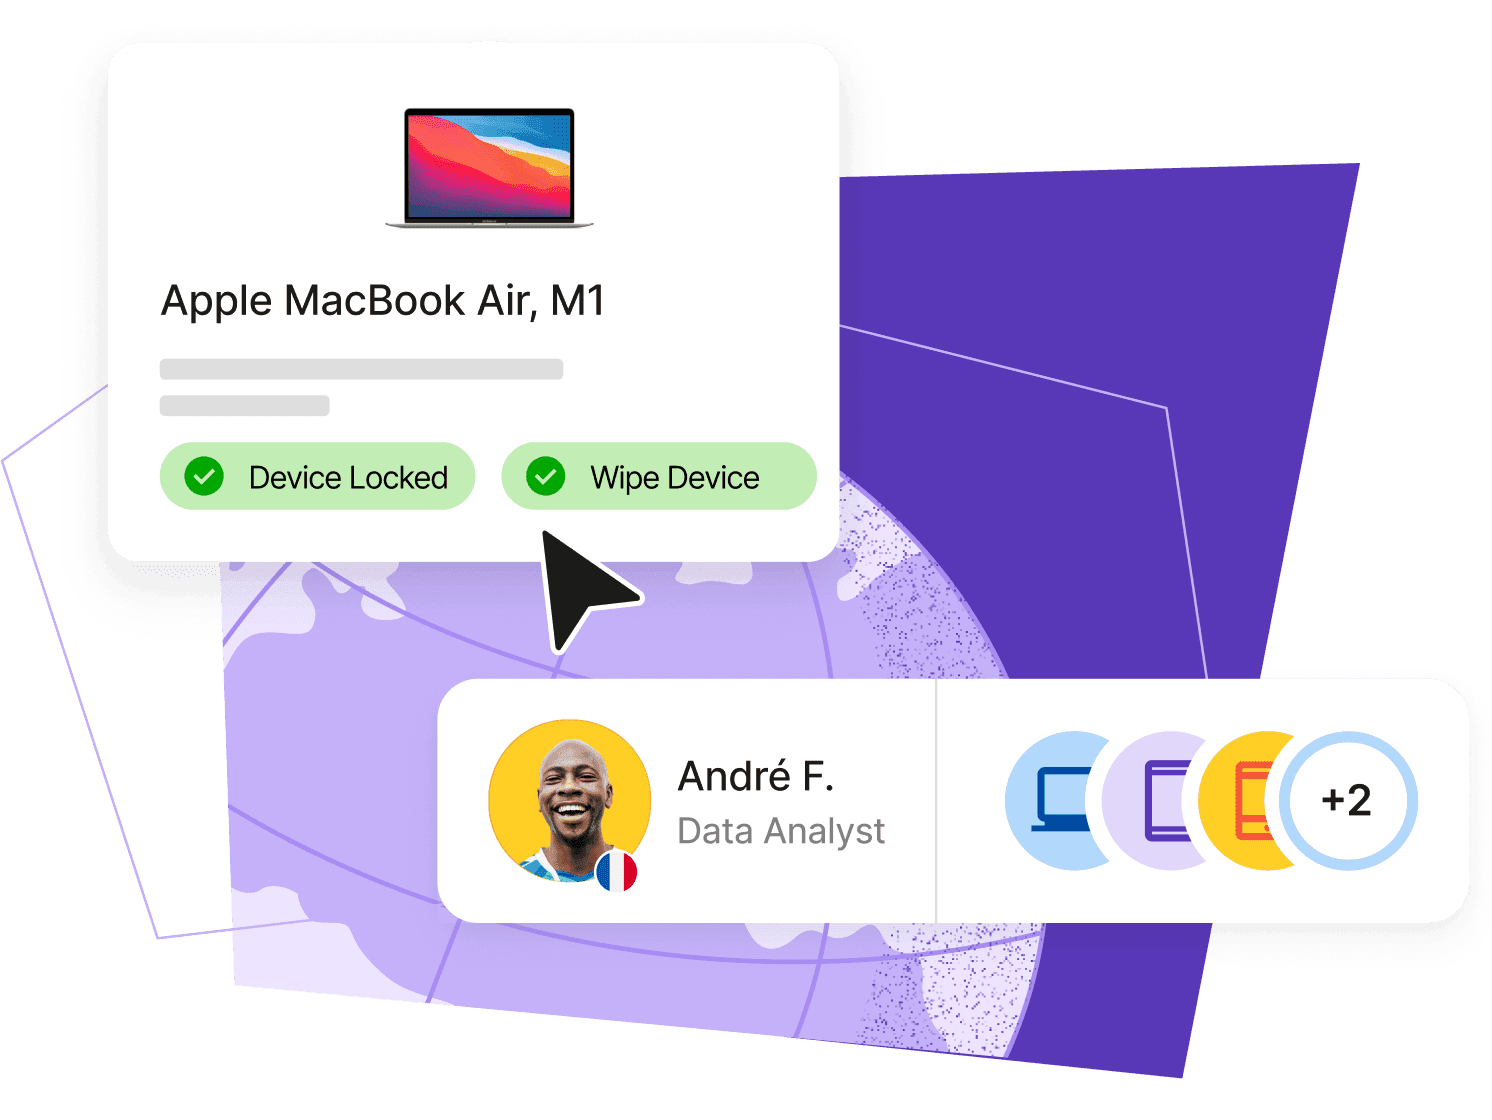
Seamlessly provision device and app access for global teams
Before an automated workflow provisions accounts for a new hire, it's also important to consider identity fraud risks. Deel Security helps businesses spot fake identities, deepfakes, and impersonation attempts during recruitment and throughout the worker lifecycle, complementing the access provisioning and deprovisioning processes managed by your AMS.
Step 5: Prevent friction and keep automation smooth
After implementing your AMS in Step 4, the next step is to ensure your automated workflows keep running reliably. Even a strong AMS can run into friction—legacy applications, complex roles, or one-off exceptions can disrupt automation.
The table below shows common challenges, best practices, and how the right AMS features help you tackle them, building on the system and workflows you've already put in place:
| Challenge | Best practice | How a well-chosen AMS helps |
|---|---|---|
| Legacy or disconnected applications | Use automation agents or connectors to handle provisioning and deprovisioning | Built-in agents automate tasks without custom scripts, reducing manual work and errors |
| Complex or overlapping roles | Define clear role-based policies first; layer attribute-based rules only where needed | Enforces standard roles, prevents conflicting access, and simplifies updates automatically |
| One-off exceptions or regional rules | Document every exception with a clear owner, expiry, and justification | Tracks temporary or exception-based access, applies expiry controls, and logs all activity |
| Security & compliance | Require multi-factor authentication, run periodic access reviews, and maintain audit logs | AMS enforces controls automatically and provides built-in reporting for audits |
| Orphaned accounts or drift | Monitor critical workflows to ensure provisioning/deprovisioning works as intended | Automatic revocation and alerts prevent lingering access and reduce administrative overhead |
Resources to strengthen access management
Building reliable provisioning and deprovisioning workflows starts with clear access policies. These free resources can help:
Access Control Policy Template: Define access permissions, approval processes, and responsibilities.
Strategic Onboarding & Offboarding Guide: Improve access management across employee transitions.
Free IT Policy Template: Establish consistent IT security and device policies.
Step 6: Plan for the next 12–24 months
Access management isn't a one-time project — it's an evolving capability that grows with your workforce and risk environment. The organizations that stay ahead focus on automation, security, and scalability from day one.
Next steps to future-proof your AMS:
Zero Trust by default: verify identity, device health, and context at every access attempt — not just at login
Least privilege first: make temporary, scoped access the default rather than retrofitting later
Smarter access reviews: use intelligent automation to flag unused or risky permissions and reduce manual work
Secure AI and data tools: apply the same access controls and audit standards to AI platforms and sensitive data as you do for other systems
Global-ready operations: design identity and device management to respect data residency and compliance across every region you operate in
Streamline automated access provisioning and deprovisioning with Deel IT
When someone joins, changes roles, or leaves your company, their system access needs to keep up. Deel IT connects employee lifecycle events with access management, device provisioning, and security workflows, helping IT teams manage these changes without juggling separate processes.
By integrating with HRIS platforms such as BambooHR, Workday, and HiBob, and identity providers including Okta, Google Workspace, and Microsoft Entra ID, Deel IT helps turn employee updates into coordinated IT actions.
Here's what you can do with Deel IT:
Automate access throughout the employee lifecycle: Trigger account provisioning, permission updates, and deprovisioning when employees join, change roles, or leave, reducing manual IT requests.
Manage access and devices together: Coordinate application permissions, device setup, security policies, and offboarding through connected workflows.
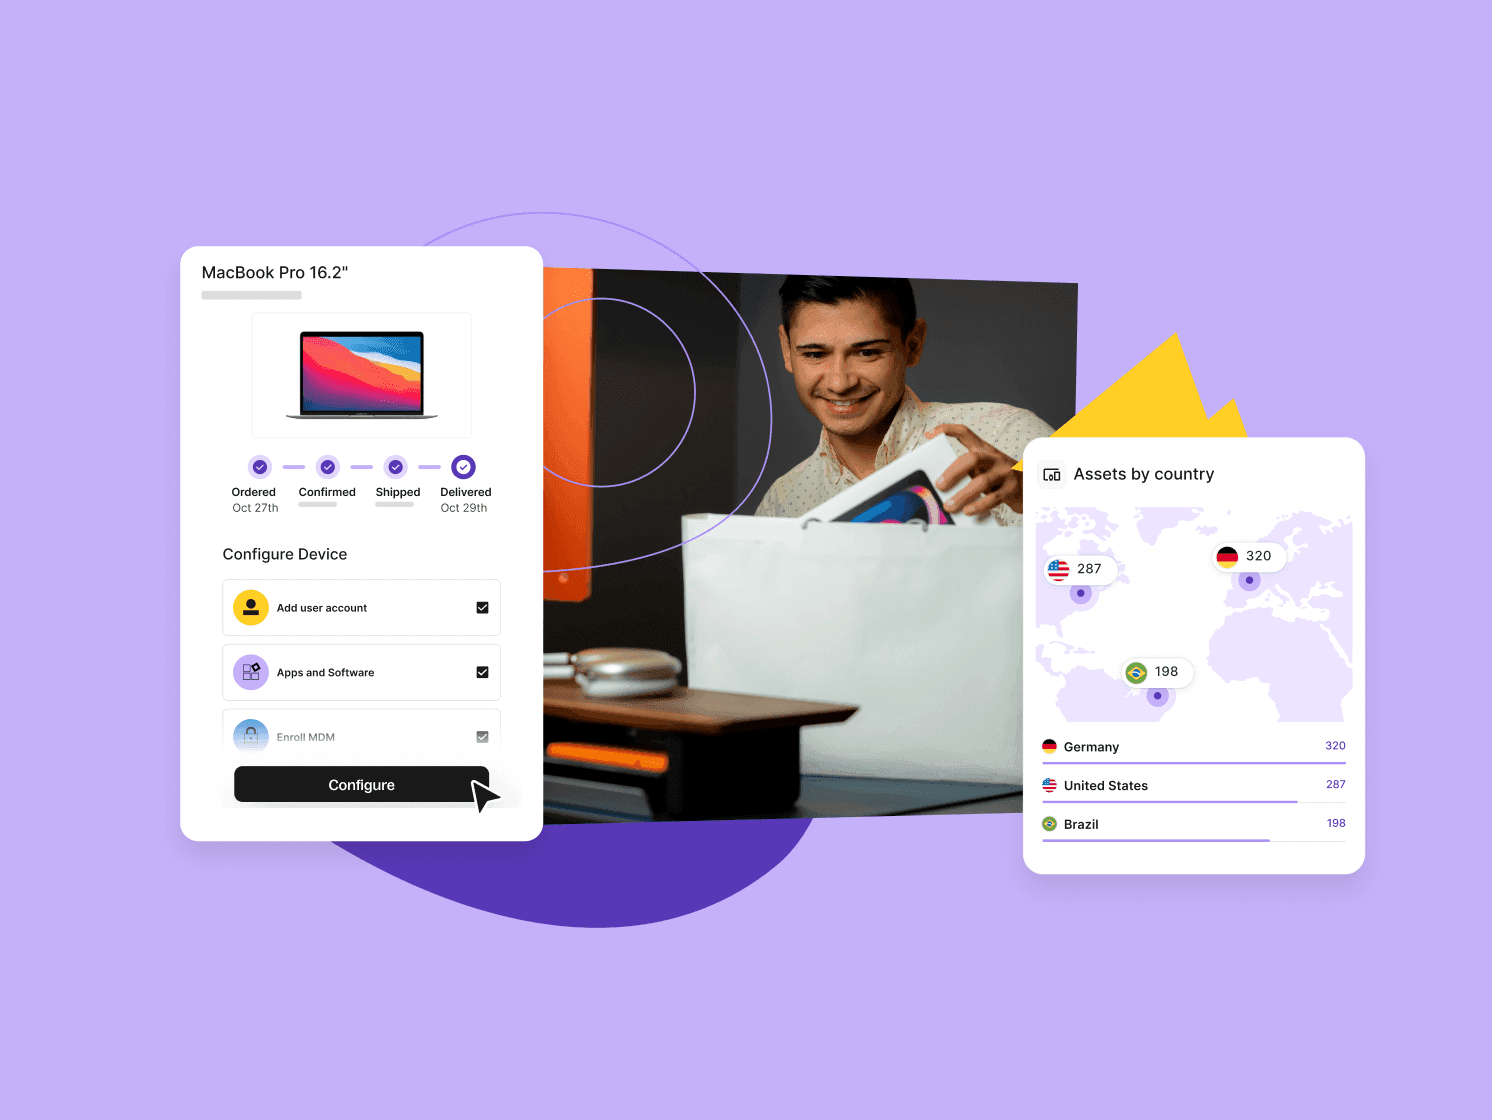
Get devices ready for new hires worldwide: Procure, configure, and deliver devices across 130+ countries, with security settings and applications prepared for onboarding.
Keep security policies consistent: Apply role-based access controls and manage device security with built-in endpoint protection powered by CrowdStrike.
Improve visibility and oversight: Track device status and connected IT workflows centrally, making it easier to spot outstanding tasks and coordinate offboarding.
Support employees around the clock: Give distributed teams access to 24/7 IT support without placing every support request on your internal IT team.
Deel IT works alongside your existing HRIS and identity providers, connecting employment changes with the IT tasks that follow. Instead of managing access, devices, and security as separate processes, your team can coordinate them as part of the same employee lifecycle.
Book a demo to see how Deel IT can simplify access provisioning and offboarding for your team.
Deel IT
Procure, deliver, manage, and secure devices anywhere
FAQ
Which access management systems can automate user provisioning and deprovisioning?
Okta and Microsoft Entra ID are established options for automating identity and application access. Deel IT offers a more comprehensive approach, connecting HR-driven provisioning and deprovisioning with device management, security, and offboarding in one coordinated workflow. This makes it a particularly strong choice for growing and distributed teams that want to simplify IT operations beyond access management alone.
What is access provisioning and deprovisioning?
Provisioning gives employees access to the applications and systems they need to do their jobs. Deprovisioning removes that access when they leave or no longer need it. Both are essential for keeping permissions accurate throughout the employee lifecycle.
Can I automate provisioning without replacing my existing identity provider?
Yes. Many organizations can keep their existing identity provider and connect it to their HR system through supported integrations. Deel IT also works alongside identity providers such as Okta, Google Workspace, and Microsoft Entra ID, helping coordinate access changes with broader IT workflows.
What happens if an application doesn't support SCIM provisioning?
You may need to use an alternative integration, API, or manual approval workflow. Check whether your access management platform supports the application and how it handles account creation and removal. Applications without automated deprovisioning should have a documented offboarding process.
How can I confirm that employee access has been removed after offboarding?
Check the completion status of deprovisioning workflows and verify that accounts have been disabled or removed in the relevant applications. Audit logs and alerts for failed actions help IT teams identify access that still needs attention.
How does role-based access control (RBAC) improve automated provisioning?
Role-based access control (RBAC) assigns permissions according to job responsibilities rather than configuring each employee individually. This makes onboarding more consistent and helps ensure permissions are updated when employees change roles.
What features should I look for in an access management system in 2026?
Prioritize HRIS and identity provider integrations, automated onboarding and offboarding, role-based permissions, support for your existing applications, and clear audit logs. For distributed teams, also consider device management, security policy coordination, and global IT support.
About the author
Dr Kristine Lennie holds a PhD in Mathematical Biology and loves learning, research and content creation. She had written academic, creative and industry-related content and enjoys exploring new topics and ideas. She is passionate about helping create a truly global workforce, where employers and employees are not limited by borders to achieve success.